Kafka for financial services: Modernize faster, with resilience
Event-driven architecture for financial services. Self-service Kafka for your teams. Compliance built-in.


Why Kafka adoption stalls for regulated financial institutions
Financial services need Apache Kafka and real-time streaming architecture to compete: real-time data, cloud platforms, and self-service teams are a must to deliver innovative services to customers. But three specific challenges stop Kafka modernization in its tracks.
Governance and compliance pump the brakes
To build event-driven applications with Apache Kafka, you need broader team access to real-time data streams. But without governance, you risk audit failures and data breaches. Most platforms force a choice: restrict access and slow modernization, or allow access and increase compliance risk. The result: Kafka adoption gets blocked by governance concerns.
Developers sit on dependencies
Teams need to move faster, but they're blocked waiting for expert help. Kafka troubleshooting and incident response require specialized knowledge, creating bottlenecks. The productivity loss is significant – but the real cost is organizational agility.
Time-to-modernize stalls
Modernizing to event-driven architecture – cloud migration, real-time pipelines, event-driven applications, AI agents – requires deep visibility into Kafka's internals. Most teams lack this visibility, causing projects that should take weeks to stretch to months.
Data streaming for financial services, with governance built-in
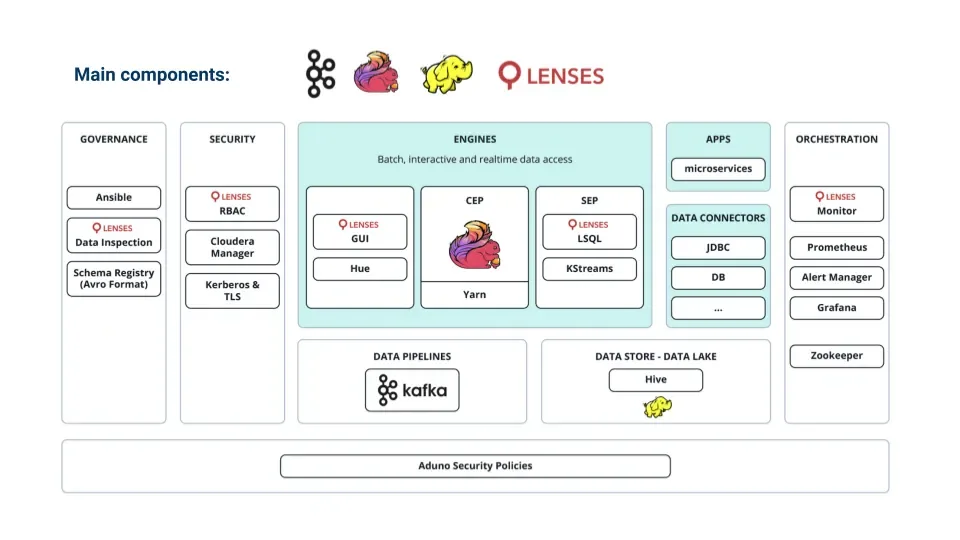
Lenses adds a governance, observability, and productivity layer on top of Apache Kafka. For regulated financial services:
Visualize your data landscape
See all your Kafka topics, applications, data flows, and dependencies across on-premises, cloud, and managed Kafka environments. Understand which applications access which sensitive data (PII, payment info, transaction history).Compliance and audit teams get complete visibility. This is your first line of audit defense.
Define governance rules once
Set role-based access controls (RBAC): data scientists, traders, and compliance teams get appropriate levels. Define masking for sensitive fields (card numbers, SSNs, account IDs). Create immutable audit trails. Rules apply uniformly to developers, operators, and AI agents. SOX, PCI-DSS, GDPR, and CCPA compliance is built-in, not added later.
Migrate data, maintain compliance
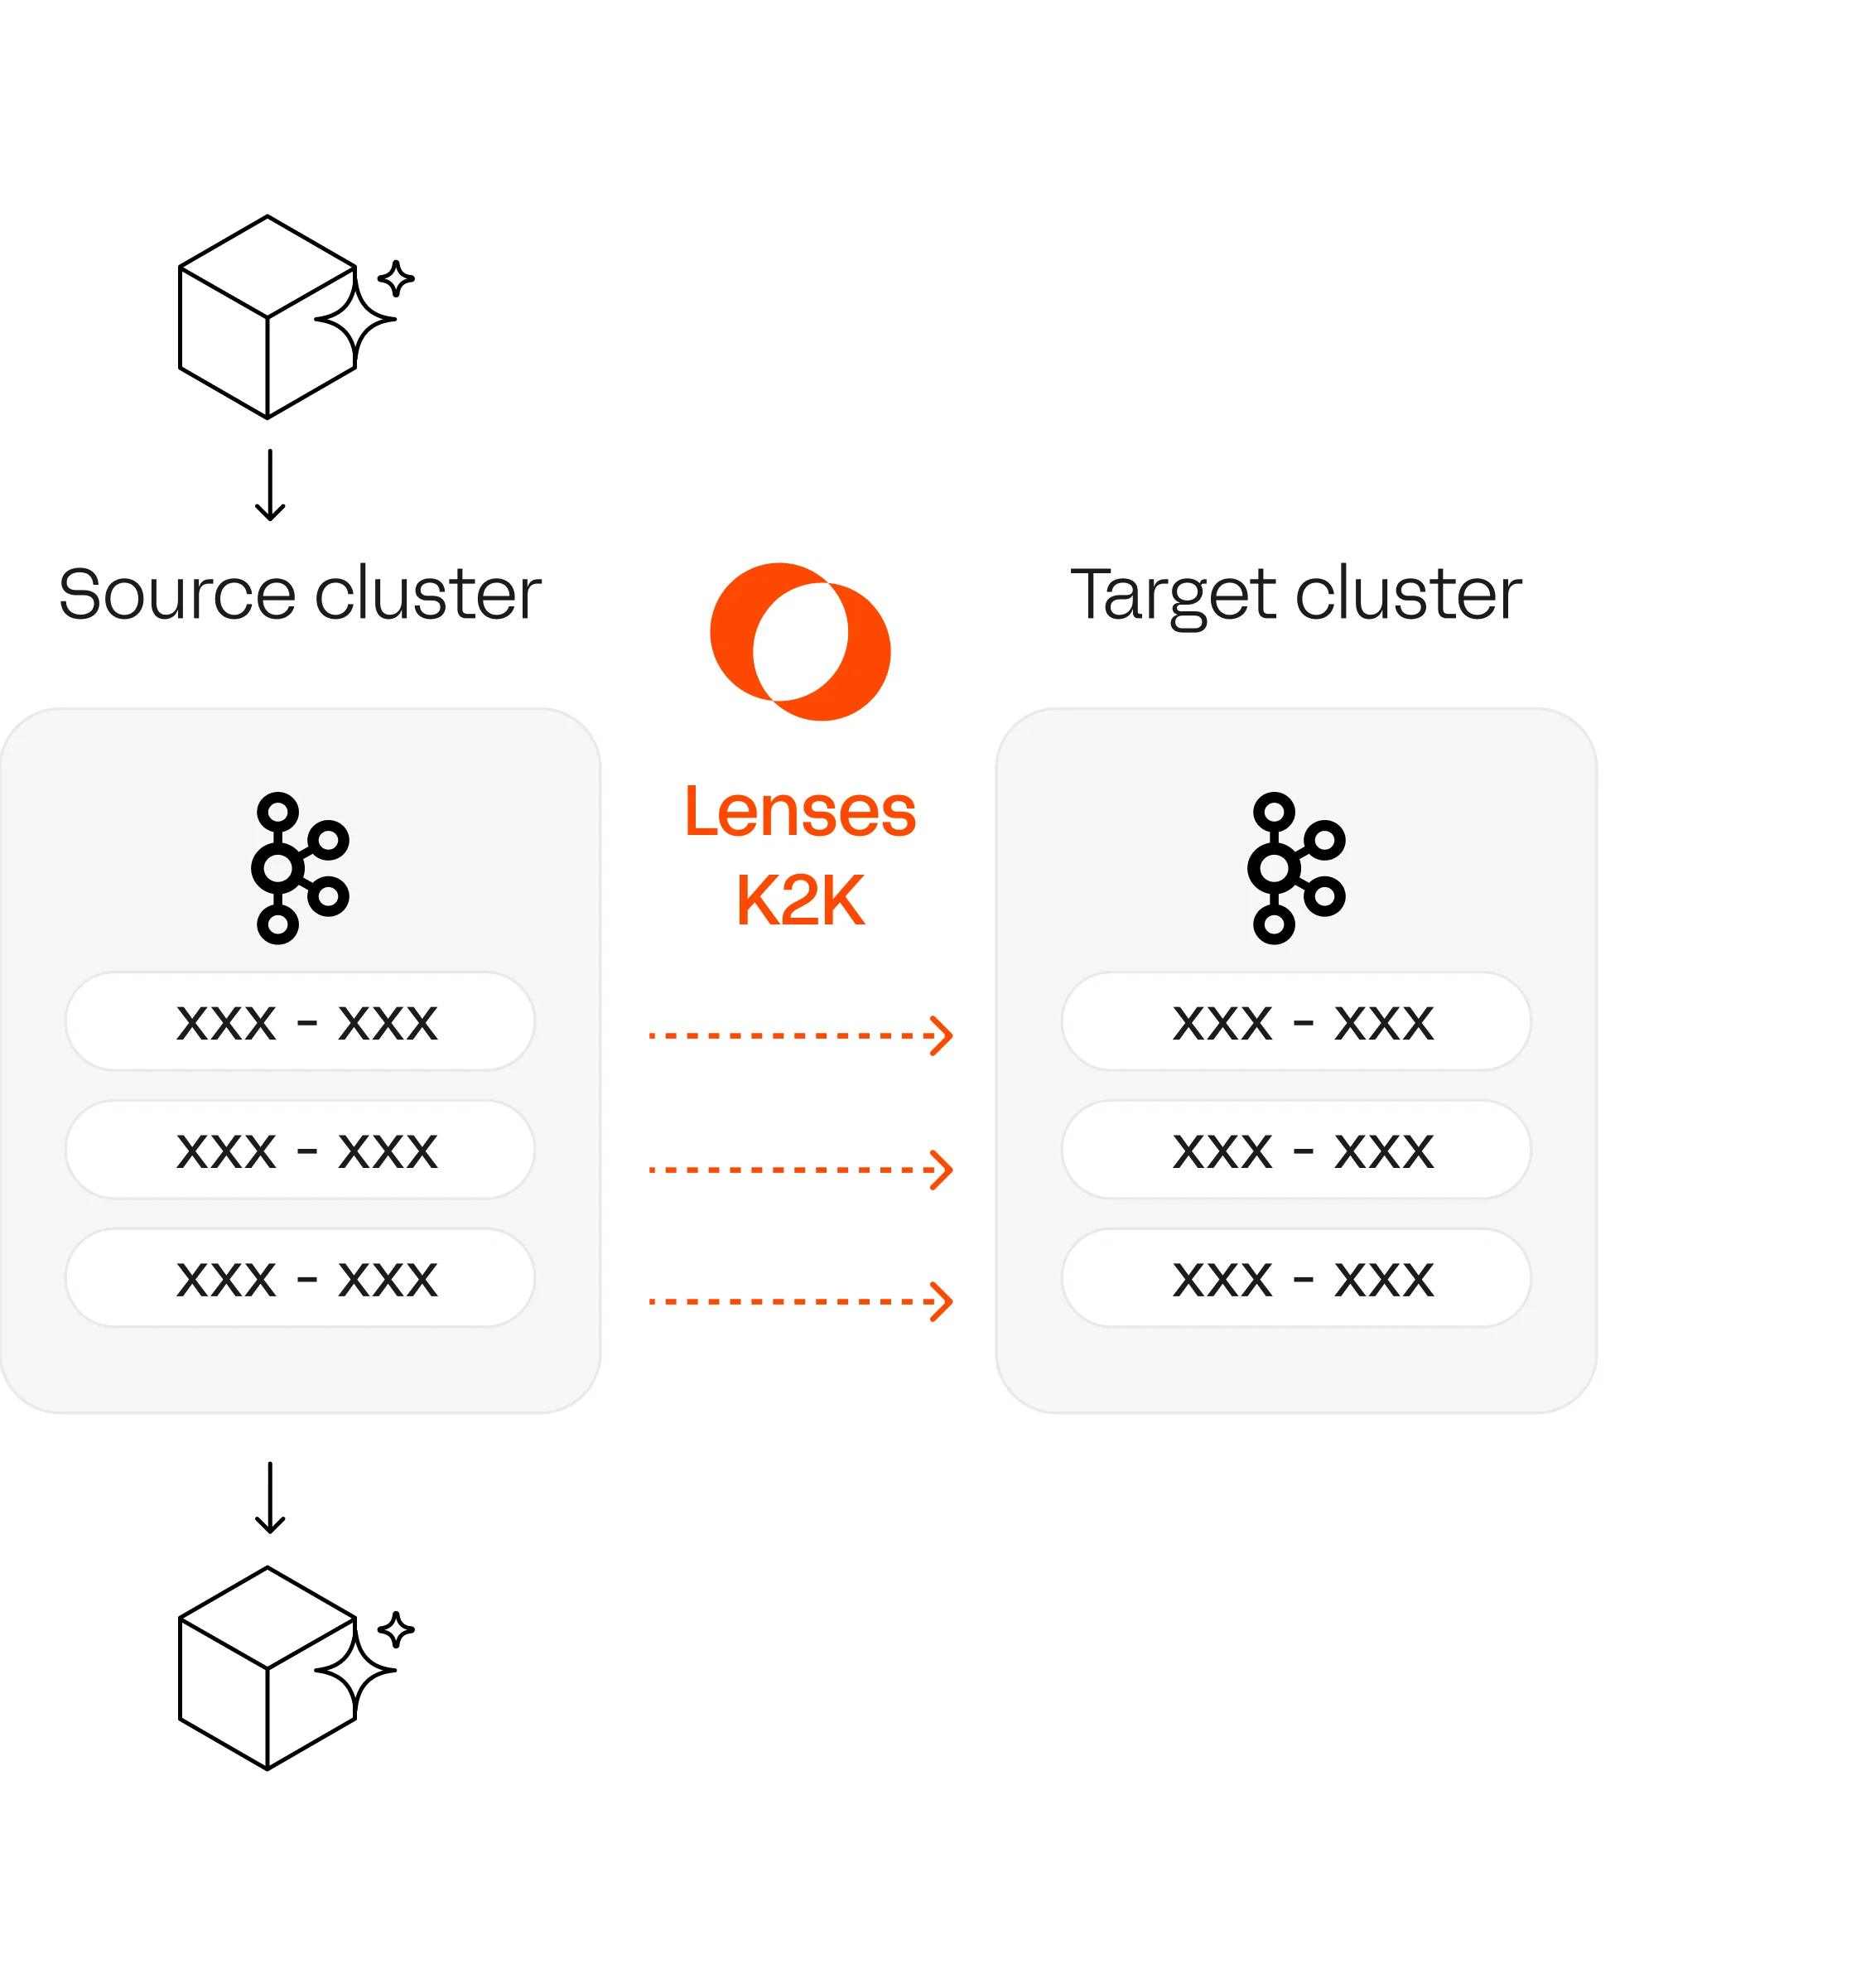
Moving between IBM Cloud, AWS, Confluent Cloud and on-prem? Lenses replicates Kafka topics, schemas, consumer offsets, and metadata across any vendor or cloud. Governance rules travel with the data; all masked and audited. Modernize without losing control, while data stays governed during migration. The audit trail remains unbroken.
Give your teams self-service access
Developers, data engineers, ops and AI agents access Kafka via a simple, governed interface or MCP. Query data with SQL, produce test messages and monitor consumer lag – all through role-based access. This reduces escalations to the platform team, while developers comply with regulations and move faster.
Troubleshoot and resolve at speed
When a pipeline breaks, investigate in minutes, not hours. Lenses shows consumer lag, poison pills, schema mismatches, and configuration drift. Full visibility means faster root cause analysis by your team or AI agents. Incidents impact revenue, and every minute of downtime costs money. Faster MTTR directly improves SLA compliance and customer experience.
Monitor and optimize continuously
Track Apache Kafka health and real-time data quality across clusters. Alerts on schema drift and consumer lag prevent cascading failures. All actions—human and agent—are auditable. Visibility prevents data quality issues from becoming compliance problems.
+€5M
annual productivity gains
Per FTE, per year, at a large global bank with 500+ developers.
−2
months per cloud migration
At 4-5 modernization projects per year.
+€100K
reduced MTTR
Annually across a 500-app Kafka estate.
−70%
audit cycle time
Via audit trails and access controls.
What makes Lenses a match for financial services?
Governance-first architecture
Built for regulated environments. Granular RBAC, immutable audit trails, automated data masking, and real-time access controls. Compliant with SOX, PCI-DSS, GDPR, and CCPA by design.
Developer autonomy with built-in compliance
Developers provision topics and access in minutes, while policies enforce data classification, audit logging, and access controls automatically. Every change is logged for regulators.
Vendor agnostic
Works on top of any Kafka: on-premises Apache Kafka, IBM Event Streams, Confluent Cloud, AWS MSK, Aiven. Migrate between any environments without replatforming.
Multi-Kafka Visibility
Manage hundreds of Kafka clusters across geographies and networks. Single pane of glass for all data flows, access patterns, and compliance status.
Agent-ready access controls
Just as developers get role-based access to Kafka, AI agents can be granted granular credentials and permissions with full auditability. Agents inherit RBAC. Every agent decision is logged and auditable.
Enterprise compliance & scale
Certified for IBM Financial Services Cloud. Designed to scale to enterprise footprints. Integrates with OAuth, SAML, Active Directory, and Keycloak.
Data streaming resources for FSI teams


Customer Stories
Delivering finance streaming applications 10x faster
How did a highly regulated Swiss payment provider move an event-driven marketing platform into production in under a year?
Read moreWatch our latest governance for Kafka webinar
To play this video, accept functional cookies in your privacy settings.
Vimeo video
Kafka migration horror stories
Even seasoned engineers are haunted by their experiences with cloud migration and modernization. No need to freak out: We help you walk away with your data intact, your applications running as expected, and your team’s sanity preserved.
Frequently asked questions
Lenses provides immutable audit trails of all access and actions, plus automated RBAC, masking, and integration with your identity provider (OAuth, SAML, Active Directory). Every action is logged with who, what, when, and why. Audit-ready for external reviews.
Yes. Define masking rules for PII, transaction data, or any sensitive field. Lenses applies masks in real-time based on user role and permissions. Audit team sees the rule, but never the raw data.
Yes. Lenses is vendor agnostic and works on top of IBM Event Streams, Apache Kafka, Confluent Cloud, AWS MSK, and other Kafka distributions. Integrates seamlessly with IBM Cloud / DMZR environments.
2–4 weeks of planning and execution per use case, down from 3–6 months with manual approaches. Automated offset translation, full visibility during cutover, and rollback capability reduce risk and time significantly.
Lenses scales to hundreds of Kafka clusters across different networks, clouds, and geographies. Designed for enterprise footprints in global financial services.
No. Lenses is a self-contained, Kubernetes-native application. No separate infrastructure to deploy or manage.
Lenses provides live side-by-side observability and rollback capability. You can validate parity between source and target, then roll back cleanly if issues arise – at any step.
Yes. Agents can be granted granular access credentials and permissions just like developers. They inherit role-based access controls, and every agent action is logged and auditable for compliance.

Move fast, with full control
Build, govern and operate Kafka apps for finance - with engineers and AI agents. One place for your whole streaming estate.

20 minute demo

- Get a guided tour of Lenses
- Receive a trial key to install on your clusters
- Perfect for production and large-scale streaming deployments